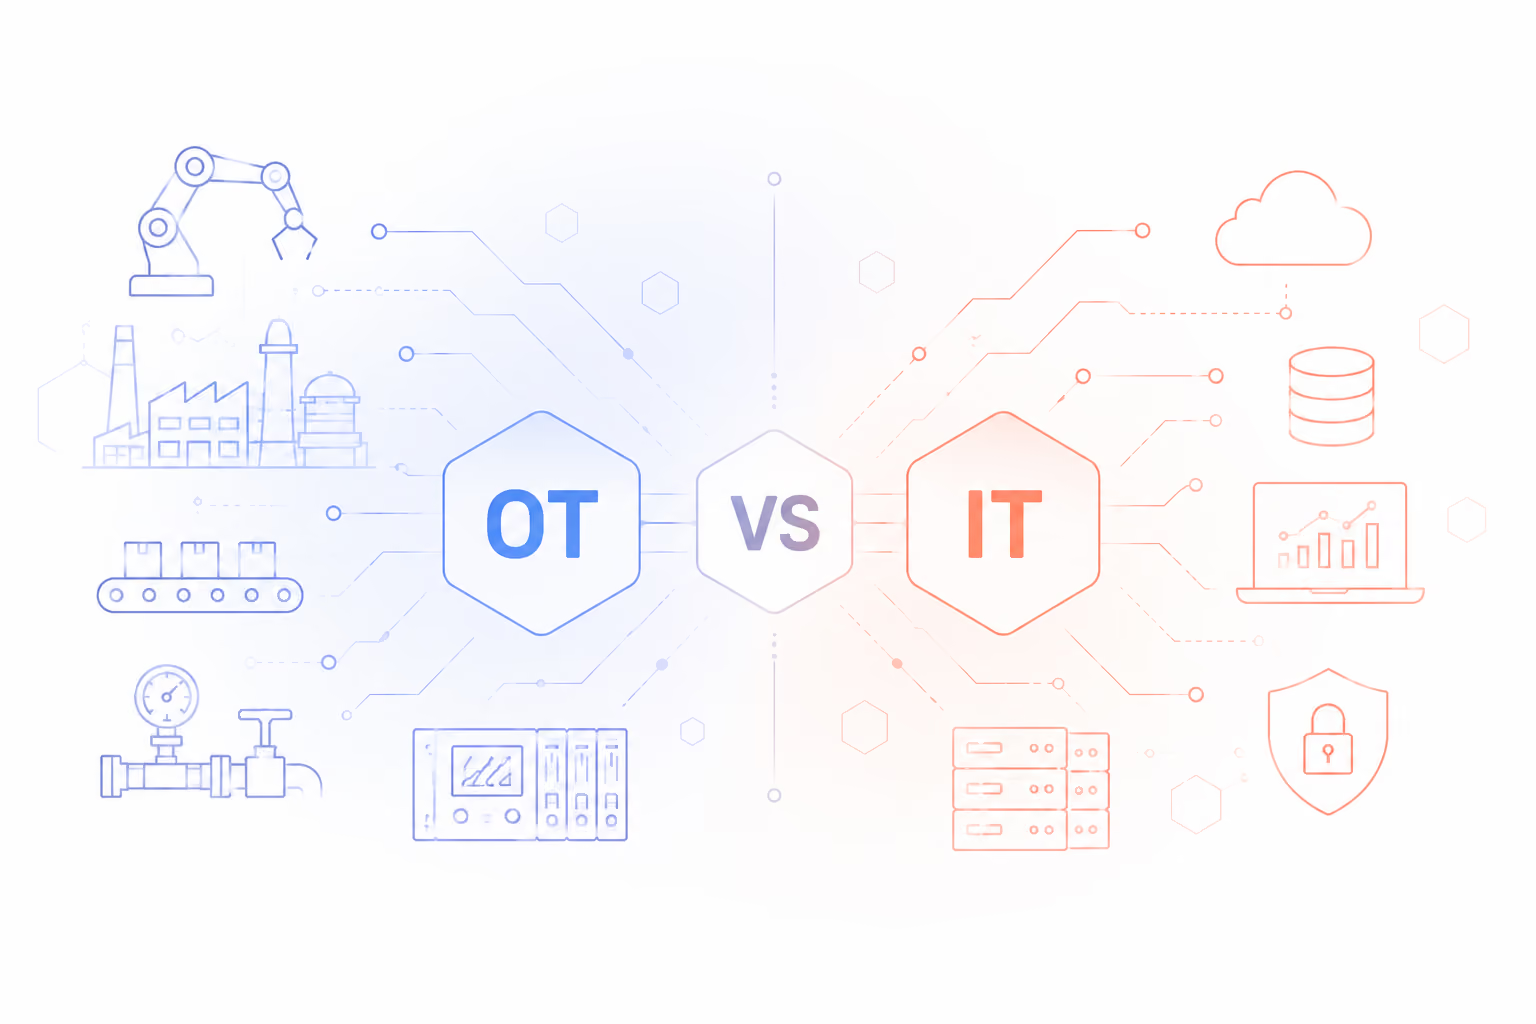
Manufacturer with office, industrial, and IoT networks across sites
A manufacturing company operating in specialized technology domains where access to experienced network and security experts is limited. Its infrastructure spans multiple production facilities, combining office systems with industrial and IoT networks that require continuous availability and strict security controls.
Keeping thousands of network endpoints available and secure
Managing industrial networks across several locations requires balancing availability, security, and operational efficiency in an environment where downtime directly impacts production. The client needed to maintain stable connectivity across thousands of network endpoints while ensuring consistent user access and enforcing security policies across all sites.
At the same time, the growing complexity of the infrastructure, combined with evolving security threats, made it increasingly difficult to monitor activity, control traffic, and respond to incidents effectively. Without centralized management and dedicated expertise, the organization faced increased operational risk and limited visibility into its network environment.
Requirements for ISO 27001-aligned network operations
To maintain control and resilience, the organization needed a solution that could:
- provide continuous operation of office and industrial (IoT) networks
- centralize configuration and network management across locations
- enforce consistent identity and access management
- monitor network activity and detect potential threats
- support scalable security practices aligned with ISO 27001
- provide expert support for ongoing operations and incidents
The goal was to create a secure and reliable network environment that could support production without disruption.
Centralized network and security management across facilities
A centralized network and security management model was implemented, combining operational support with structured security practices aligned with ISO 27001 standards. Instead of managing each location independently, the infrastructure is controlled through a unified approach that ensures consistency across all facilities.
The solution integrates network management, user authentication, and security controls into a cohesive system, enabling better visibility and control over traffic and access. At the same time, expert support ensures that the system is continuously maintained, monitored, and improved, reducing the burden on internal teams.
Technology stack:
- Extreme Networks for network infrastructure
- Fortinet for security and traffic management
- UTM / NGFW solutions for network protection
How Active Directory and 802.1X control network access
Network infrastructure across all facilities is managed through a centralized configuration system, allowing consistent deployment of policies and updates. User access is controlled through integration with Active Directory and secured using protocols such as 802.1x, ensuring that only authorized users can access network resources.
Traffic between VLANs and external networks is monitored and controlled using advanced security solutions, enabling segmentation and protection of critical systems. Continuous monitoring allows potential issues to be identified early, while operational support ensures rapid response to incidents and user needs.
Key capabilities:
- Centralized management of multi-site network infrastructure
- Secure user authentication via Active Directory and 802.1x
- Network segmentation and traffic control across VLANs
- Continuous monitoring of network performance and security
- Support for office and industrial (IoT) environments
- Alignment with ISO 27001 security practices
More stable networks and faster incident response
The introduction of centralized management and dedicated expertise significantly improved network stability and visibility across all facilities. Operations became more predictable, with faster response to issues and more consistent enforcement of policies.
At the same time, improved security controls reduced exposure to threats, while better user management ensured smoother access to systems across locations.
Results: operational continuity and ISO 27001-aligned security
The solution delivered measurable improvements across key areas:
- Improved operational continuity, minimizing risk of downtime
- Stronger network security, aligned with ISO 27001 standards
- Centralized control, reducing complexity across multiple sites
- Faster incident response, through continuous monitoring
- Improved user access management, across facilities
- Increased organizational resilience, in a complex network environment
The next phase of development includes the establishment of a Security Operations Center (SOC), which will further enhance incident detection and response capabilities. This will allow the organization to manage security events across all systems in a more structured and proactive way, strengthening long-term resilience.
Frequently asked questions
How can 802.1x and Active Directory control network access across multiple industrial sites?
By tying 802.1x authentication to Active Directory, so only authorized users can access network resources at every site. Because identities are managed centrally, access policies stay consistent across facilities. In this project, InTechHouse integrated user access with Active Directory and secured it with 802.1x across the manufacturer's production facilities, covering both office and industrial (IoT) networks.
How is traffic between VLANs secured in a manufacturing network with IoT devices?
With network segmentation and traffic control through UTM / NGFW security solutions. Segmentation protects critical systems by monitoring and controlling traffic between VLANs and external networks. In this project, InTechHouse used Fortinet for security and traffic management on top of Extreme Networks infrastructure, with continuous monitoring so potential issues across the manufacturer's facilities are identified early.
What comes after centralized network management in an industrial network security program?
A Security Operations Center (SOC) is the planned next phase for this manufacturer. A SOC handles security events across all systems in a more structured and proactive way. In this project, InTechHouse first centralized multi-site network management aligned with ISO 27001 practices, which improved operational continuity and incident response, and the SOC will extend incident detection and response capabilities.
We’ll review your goals, technical constraints, and opportunities to design a solution that fits your organization.
Planning a data platform, analytics system, or AI solution? Our team can help design scalable architectures and deliver production-ready solutions tailored to your business.